Transform
Make your app ready for real users
Built by a vendor who left, or quickly with AI tools? We find what's risky, fix it in order of priority, and add the tests and deployment process that keep it stable, without throwing away what already works.
- high
Security
Fix first: secrets and login
- medium
Tests
Cover sign-up and payments
- medium
Deployment
Add staging and a pipeline
- low
Monitoring
Add error alerts
- OK
Documentation
Runbook in handover
It worked in the demo. Now it has real users.
Security gaps you can't see.
Exposed keys, weak login, data any user can read, and no record of who did what.
Every fix breaks something else.
No automated tests, no documentation, and nobody left who knows why it was built that way.
It can't grow.
Slow pages, failed payments, and outages as soon as usage climbs.
What we do
Audit first, then fix what matters most
We start with a paid Code & Architecture Audit, so you know exactly what you have. Then we fix problems in order of risk: security first, then stability, then the tests and deployment pipeline that stop problems from coming back. We keep the parts that work. If rebuilding part of the app is cheaper than fixing it, we show you the numbers and you decide.
- Security fixes: secrets, login, permissions, and data exposure
- Stability fixes for the failures your users actually hit
- Automated tests around the features that matter most
- A deployment pipeline with a staging environment, so releases stop being risky
- Monitoring and error alerts
- Documentation, so the next developer, ours or yours, can work on it
What you get
Audit report
Findings ranked by severity, with an estimate to fix each, delivered through the Code & Architecture Audit.
Prioritized fix plan
What to fix now, next, and later, with a fixed price for the first phase.
Hardened app
Security and stability fixes delivered and verified.
Test suite
Automated tests that protect the critical paths, such as sign-up, login, and payments.
Staged deployment
A staging environment and a pipeline that promotes tested builds to production.
Handover pack
Architecture notes, a runbook, and all accounts and access in your control.
How it works
- 11–2 weeks
Audit
A Code & Architecture Audit of the code, hosting, and data, ending with a ranked list of findings.
- 2
Plan
Agree what to fix first, and a fixed price for that phase.
- 3
Secure
Close the most serious security gaps first.
- 4
Stabilize and test
Fix the failures users hit, and add tests around the critical paths.
- 5
Ship safely
Set up staging, the deployment pipeline, and monitoring, then hand over or move to Managed Services & Support.
The length of the fix phase depends on the audit findings; we quote it at a fixed price before starting.
The same work, in systems we run every day
Hardening is ongoing work in the platforms we build and operate: a claims platform in production since 2020, a security issue caught in QA, and a first-generation system rebuilt.
6 years
Continuous production service for a health insurance claims platform, 2020 to 2026, with ongoing releases
Release history: first release October 2020, about 40 tagged releases since
766
Automated tests on the livestock insurance rewrite across 145 endpoints and 24 controllers
Source
1,400+
Automated tests across 12 backend modules and about 100 API endpoints on our AI agent platform
Source
Scoped token
The shared tablet exchanges the manager session for a kiosk-only token, so it never holds an admin credential
Security finding resolved in QA, July 2026
Case study
Health Insurance Claims Administration Platform
Recent hardening: finer claim states before payment, more robust enrollment batches, reliable letter delivery, and a staging-to-production pipeline.
Case study
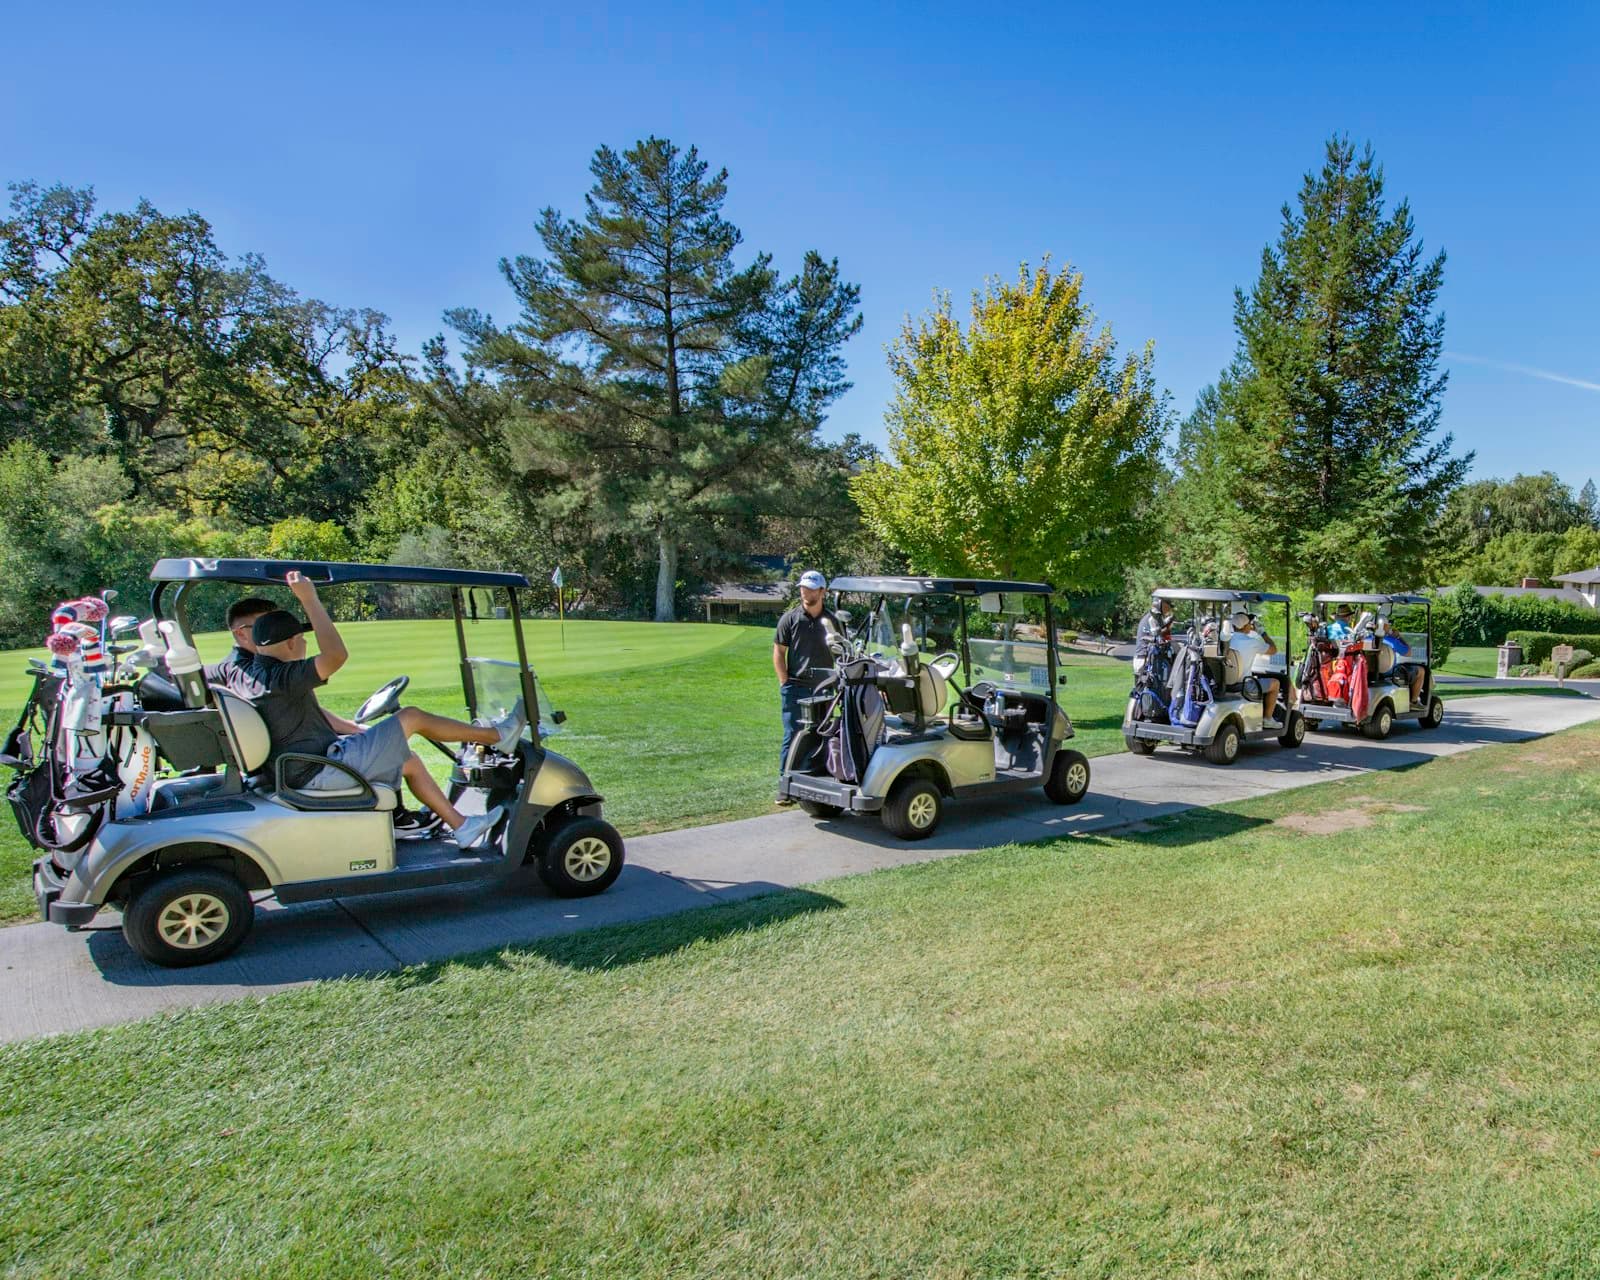
Golf Course Operations Platform
A shared crew tablet would hold a manager's session; we replaced it with a scoped, kiosk-only token.
Case study
Livestock Insurance Management System
A system that had grown hard to extend, rebuilt on a modern stack with a large automated test suite and its production data migrated.
Why Biznovelty
No rewrite pitch.
We keep what works and fix what's risky. Rebuilding is a choice we explain with numbers, not a default.
Security first.
The first fixes close the gaps that could hurt your customers or your business.
Tests and pipelines are part of the fix.
So the same problems don't come back.
We can stay.
After the rescue, we can run and extend the app on a monthly plan.
Engagement & pricing
Step 1: Code & Architecture Audit
Fixed price. The fee is credited against the fix work if you go ahead.
Step 2: Fixed-price first phase
Quoted from the audit findings.
Step 3 (optional): Managed Services & Support
A monthly plan to keep the app secure, updated, and improving.
Frequently asked questions
Yes. AI-generated code is code, and we review it like any other. These apps often work well in a demo and need security, testing, and deployment work before real users can rely on them.
Tell us what's going wrong
In a 30-minute call we'll tell you whether an audit makes sense for your app and what it would cost.