Advise & Run · 1–2 weeks
Know what you really own before you invest, take over, or scale
An independent, fixed-price review of an inherited, vendor-built, or AI-built system. In 1–2 weeks you get findings ranked by severity, a clear view of security, architecture, and maintenance cost, and a remediation plan with estimates.
- high
Access control
No role check on admin routes
- high
Secrets handling
API keys in the repository
- medium
Test coverage
No tests on payment paths
- low
Dependencies
Some libraries out of date
- OK
Backups
Restores tested
Most software risk stays invisible until it isn't
You inherited it.
The vendor or freelancer moved on, the documentation is thin, and nobody can say what will break if you change something.
It was built fast.
AI coding tools make it easy to ship an app that works in a demo. Security, access control, error handling, and tests are where it usually falls short.
A big decision depends on it.
An investment, an acquisition, a large customer, or a scaling plan rests on software no one has independently checked.
What we do
An independent review, in plain language and full detail
We read the code, run the system, and review its architecture, infrastructure, and security. We combine automated scanning with manual review by senior engineers, and we talk to whoever knows the system best. You get two things: a short summary your leadership can act on, and a detailed report your engineers can work from.
- Read-only access only; we don't change your code during the audit
- Automated scans plus manual review of the parts that matter most
- Security, architecture, code quality, tests, scalability, and operations
- Every finding ranked by severity, with evidence
- A remediation plan with effort estimates, yours to give to any team
What you get
Findings ranked by severity
Each issue with its evidence, its business impact, and how urgent it is.
Security review
Authentication, access control, secrets handling, data exposure, input handling, and outdated or vulnerable dependencies.
Architecture review
How the system is structured, where it is fragile, and whether it fits where the business is going.
Code quality and test coverage
How easy the code is to change safely, and how much of it is protected by automated tests.
Scalability and operations
What breaks first under more users or data, and how the system is deployed, monitored, and backed up.
Maintenance cost estimate and remediation plan
What it will take to keep the system running, and a prioritized fix plan with effort estimates.
How it works
- 1Days 1–2
Scope and access
Sign an NDA, agree the scope, and get read-only access to the code repository, documentation, and a staging environment or copy.
- 2Days 2–7
Review
Run automated scans and manually review security, architecture, data handling, and the most business-critical code paths.
- 3Days 7–9
Verify
Reproduce key findings safely in staging and check our understanding with your team or the original developers.
- 4Final days
Report and readout
Deliver the summary, the detailed report, and the remediation plan, and walk your team through them.
Typical duration: 1–2 weeks, depending on the size of the system.
The standards we check against are the ones we build to
We haven't published an audit case study yet. These are examples of the engineering standards we hold our own production systems to, and the same things we look for when we review someone else's.
177
Functional requirements, each traced to code by requirement ID
Specification and project README
28 tables
Under row-level security, so tenant isolation is enforced by the database, not the application
Schema migrations and database rule tests
766
Automated tests on a platform rewrite, across 145 endpoints and 24 controllers
Source
Scoped token
A shared tablet exchanges the manager session for a kiosk-only token, so it never holds an admin credential
Security finding resolved in QA, July 2026
Case study
CSat: Customer Satisfaction and NPS Surveys
Related work: every requirement ID appears in code and test names, and tenant isolation is enforced by database row-level security, with a test that checks the rules still exist.
Case study
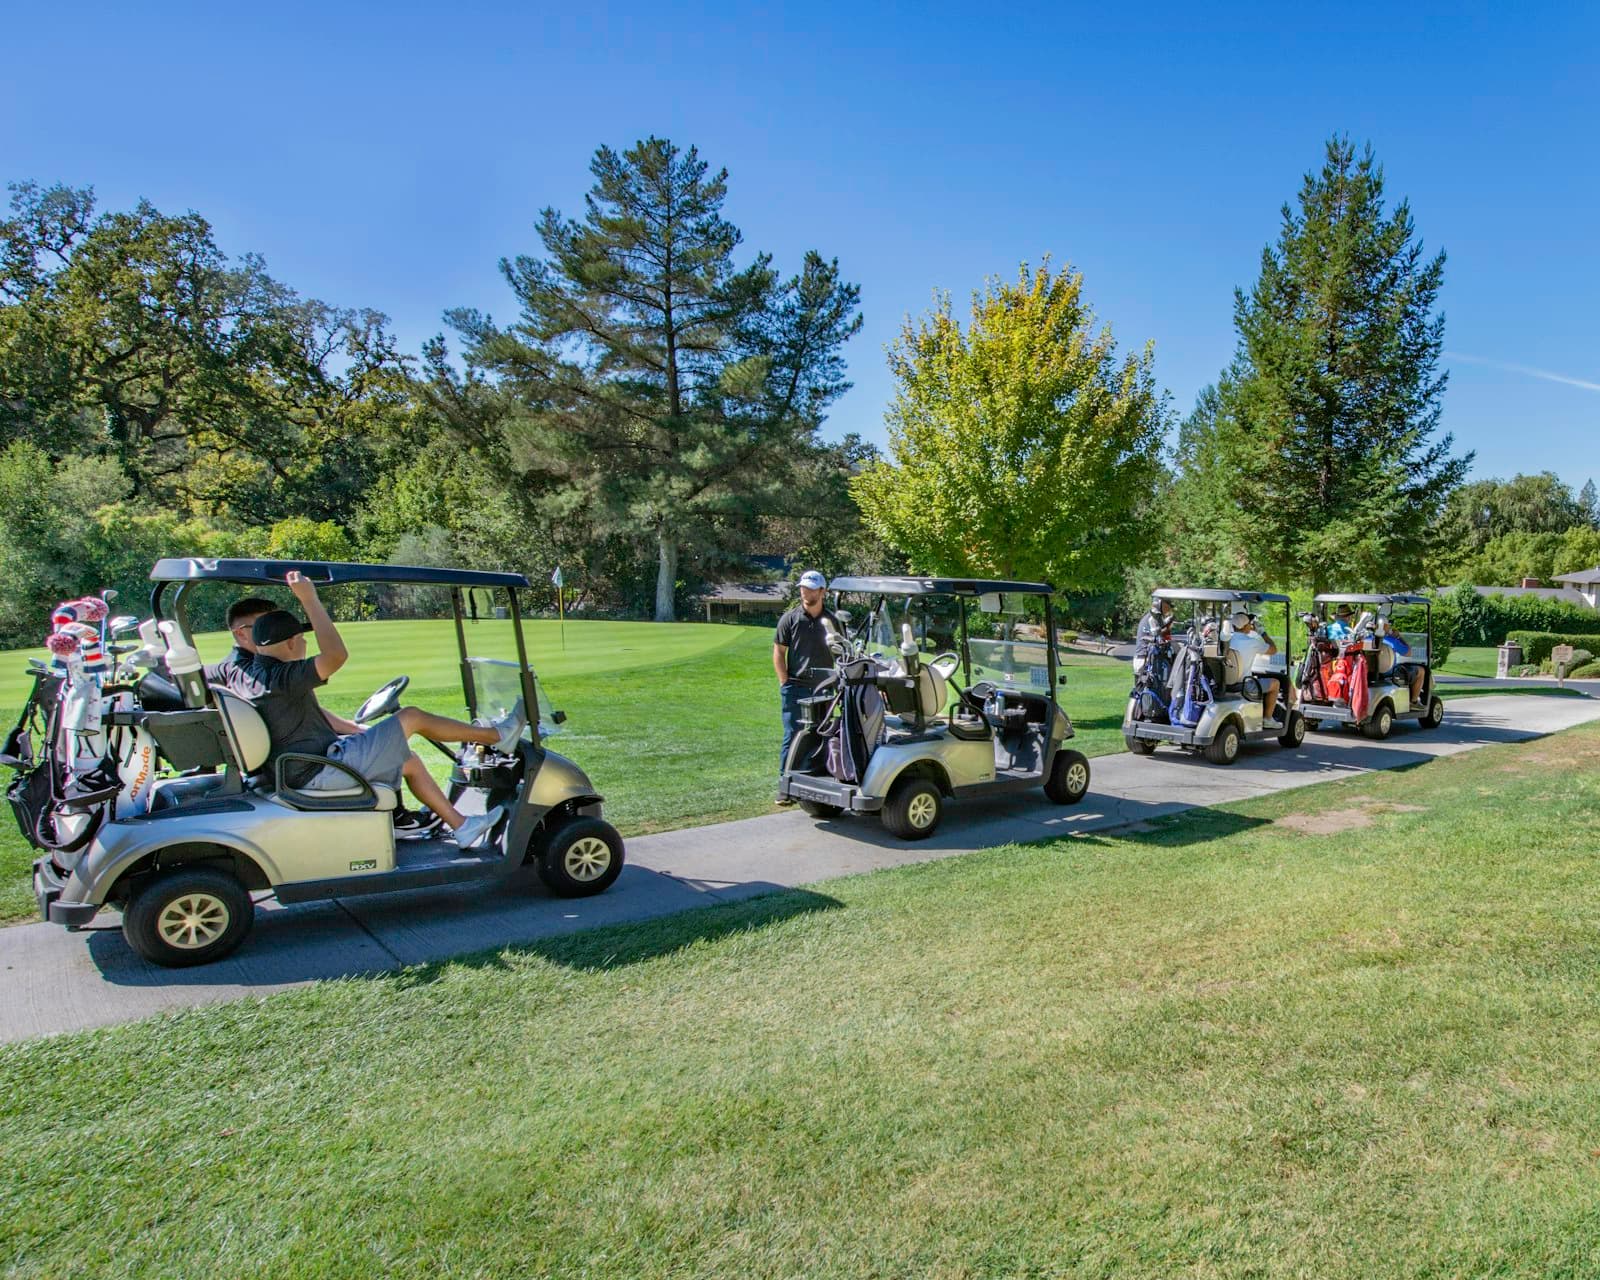
Golf Course Operations Platform
Related work: QA found a shared shop tablet holding a manager's session; it now uses a kiosk-only token and never holds an administrator credential.
Case study
Livestock Insurance Management System
Related work: the data migration produced an exceptions report listing every record that needed a human decision.
Why Biznovelty
Builders, not just reviewers.
We build and run production systems for insurers and other operations-heavy businesses, including one in continuous production since 2020.
A report anyone can use.
The remediation plan is yours. Give it to your current team, another vendor, or us.
Plain language for decision-makers.
The summary explains risk in business terms; the detail stays in the technical report.
We know where fast-built code breaks.
Authentication, secrets, input handling, and missing tests are where apps built in a hurry, by people or AI tools, most often fall short.
Engagement & pricing
Fixed price, fixed scope
Priced by the size and complexity of the system, agreed before we start. Quoted after a 30-minute call.
Read-only and confidential
NDA first; read-only access; no production access required.
Credited if you continue
The fee is deducted from App Rescue & Hardening or a Managed Services & Support agreement if you go ahead with us.
For investors
We can deliver the report to an investor or acquirer, with the company's consent.
Frequently asked questions
Read-only access to the code repository and any documentation, plus a staging environment or a copy of the system we can run. We don't need production access.
Get an independent view of the software you depend on
In a 30-minute call we'll agree the scope, the access we need, and what the audit would cost.